For small & mid-sized organisations

Cyber resilience without enterprise complexity.

ThreatInsights gives smaller teams a practical way to reduce cyber risk: attack-surface monitoring, incident response playbooks, tabletop scenarios, incident recording and action tracking in one place.

We are passionate about helping organisations improve their security, and we know not every business has a huge enterprise budget or a full cyber team.
Attack surface monitoringHigh priority
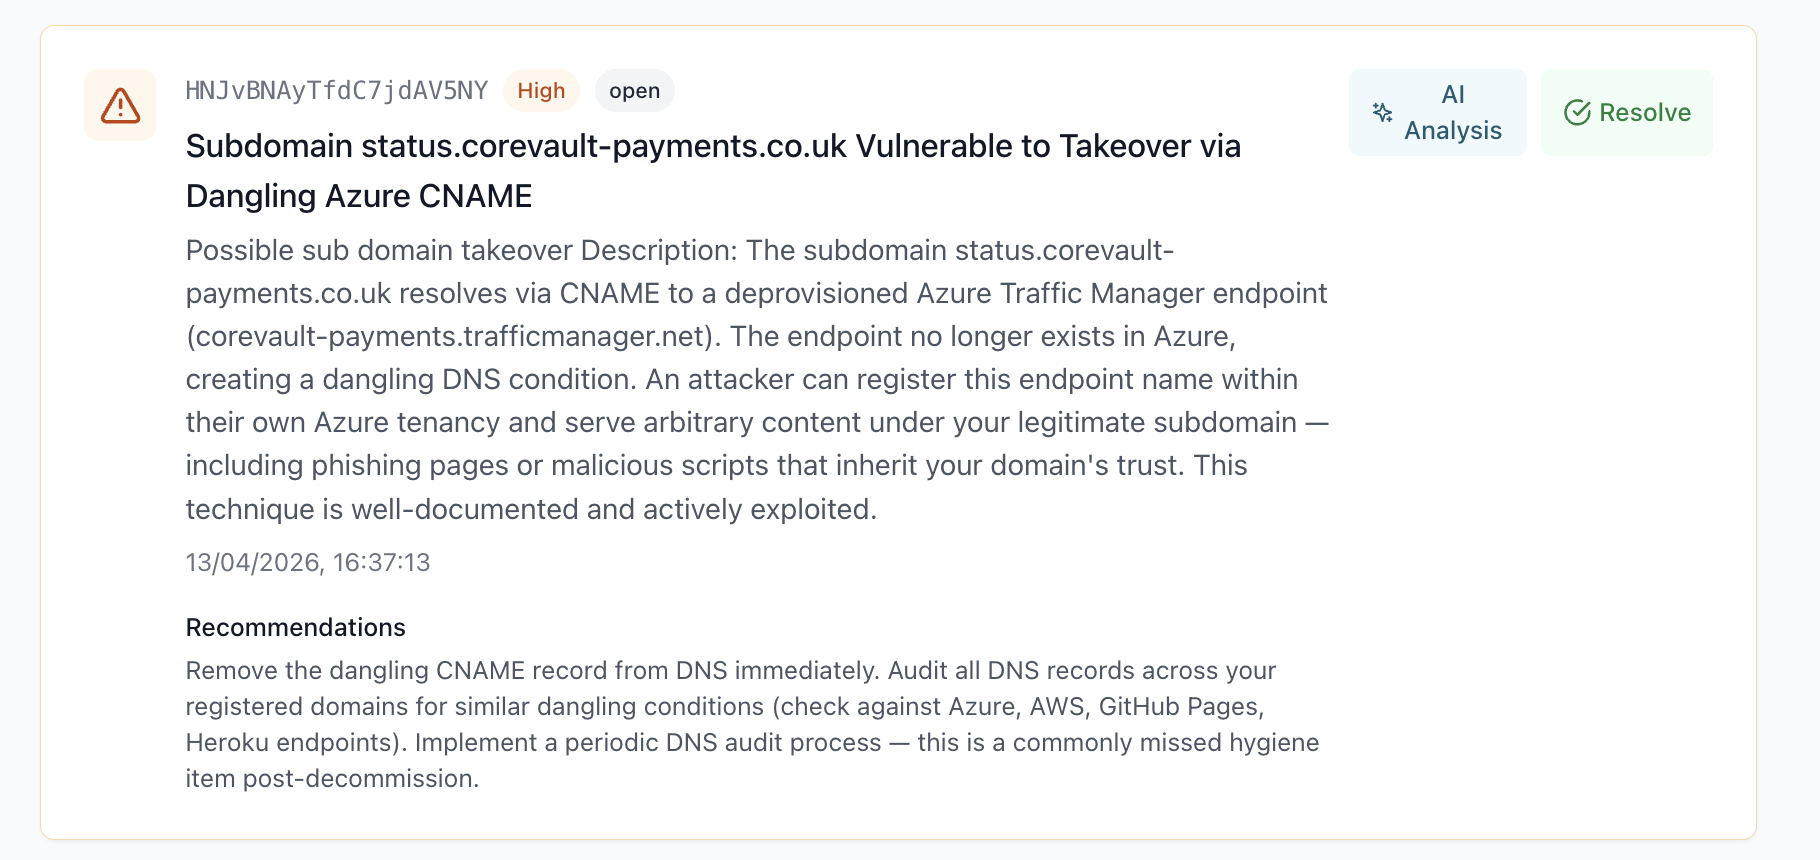
Attack surface monitoring alert showing a dangling Azure CNAME subdomain takeover risk
Incident recordingEvidence retained
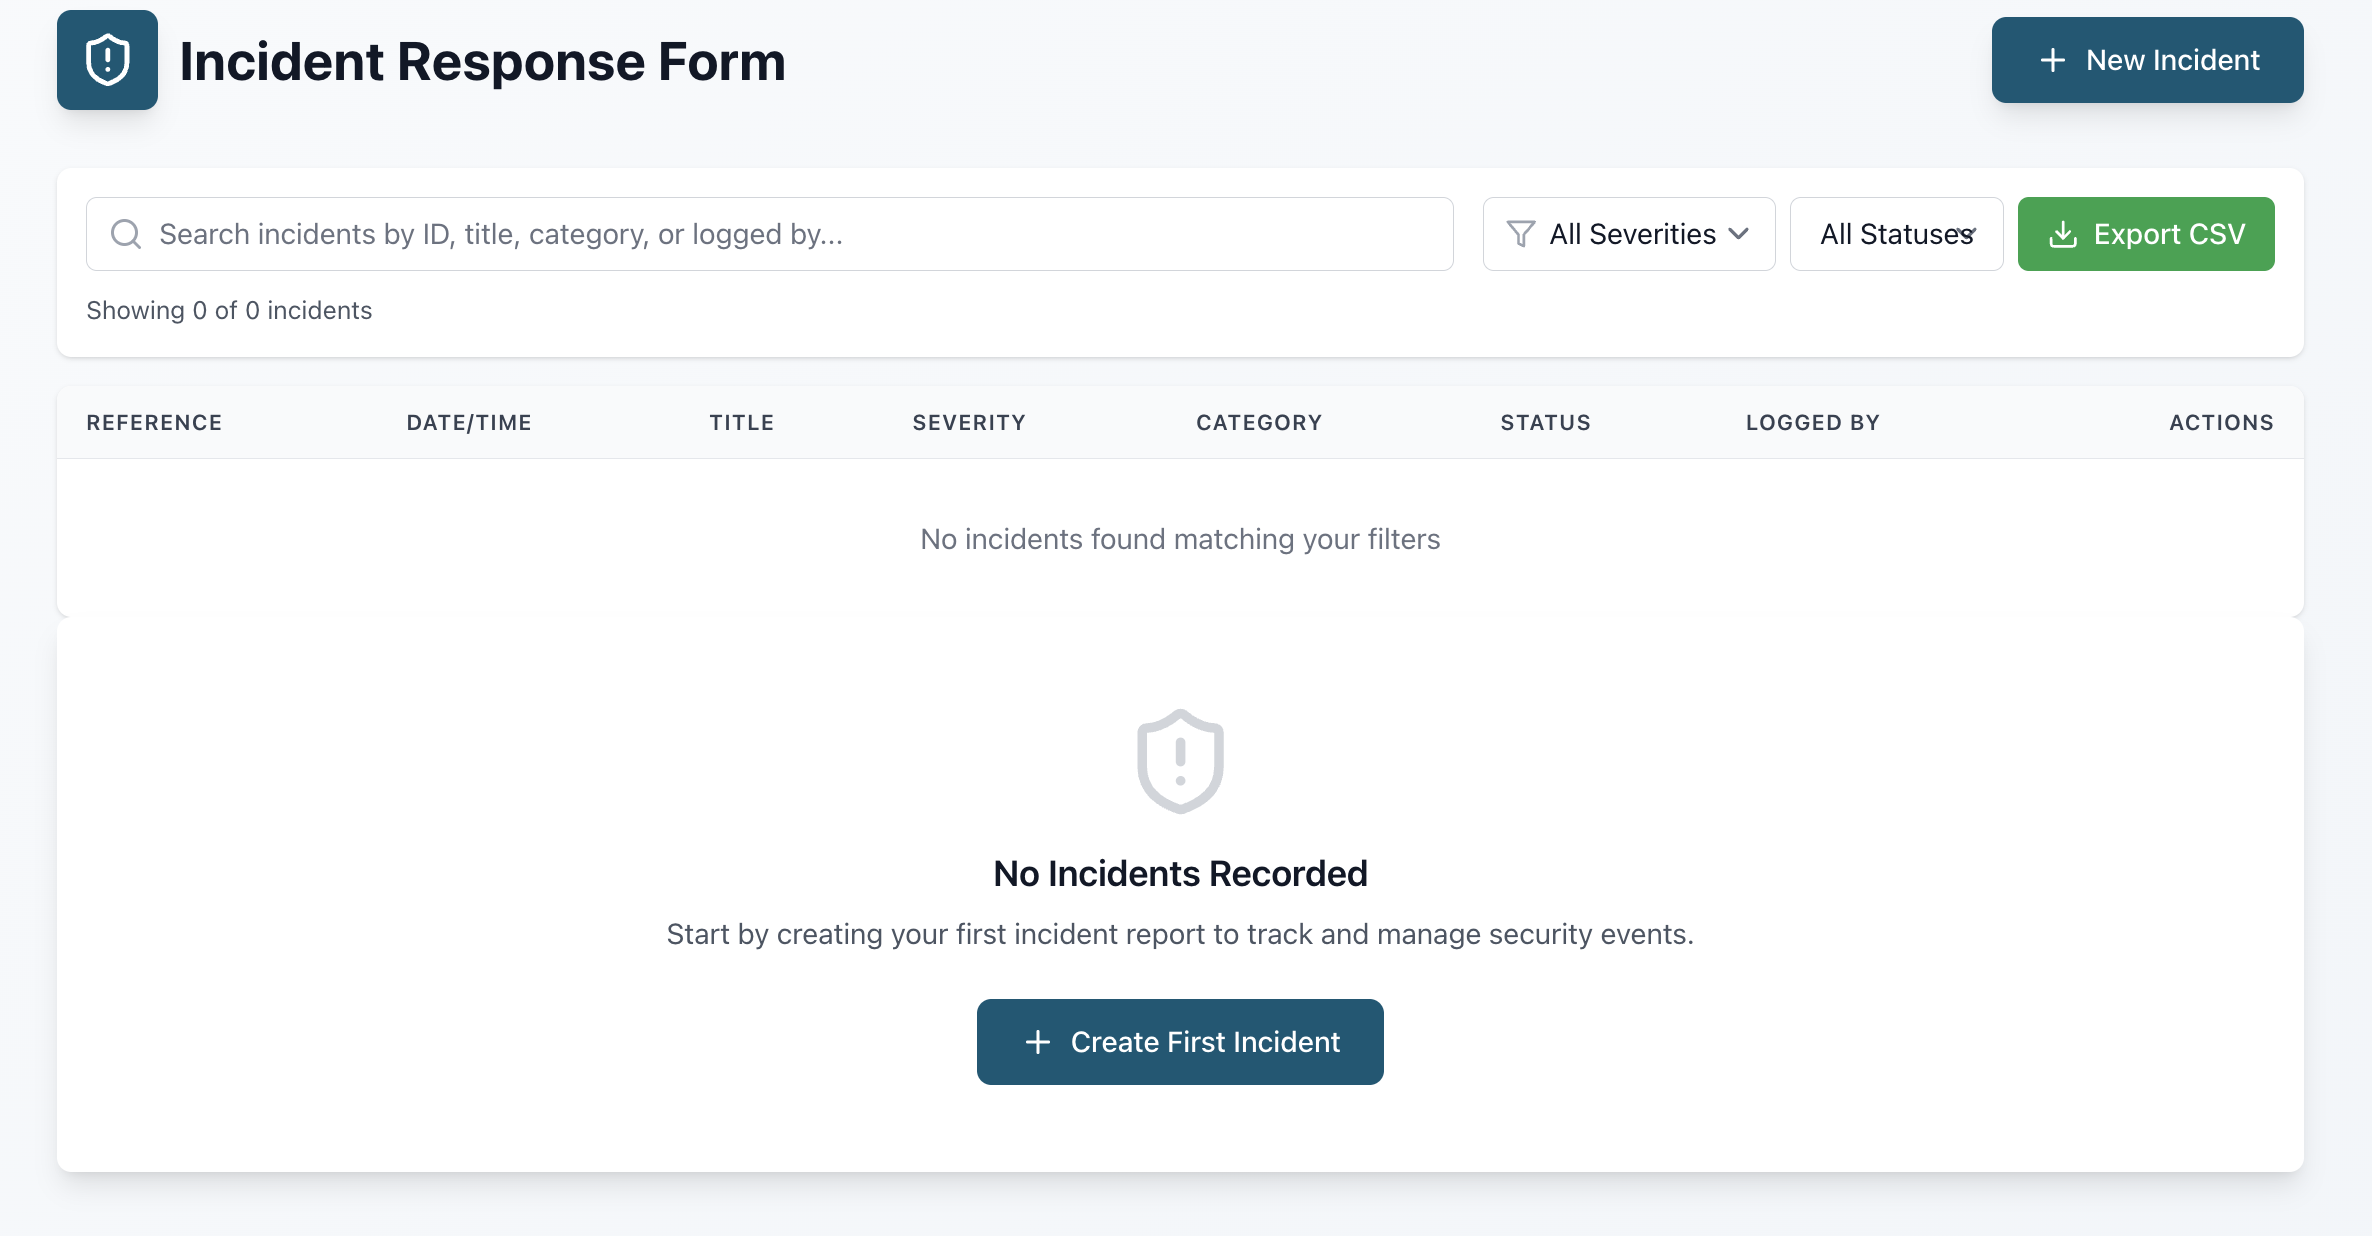
Incident response recording dashboard with filters, status and export options
External exposure monitoring Response playbooks Tabletop scenarios Incident recording Remediation tracking

The platform

Know what is exposed. Know what to do. Prove you practised.

Built for organisations that need practical security improvement without buying an enterprise stack or building a full in-house cyber function.

01

Attack surface monitoring

Track exposed services, risky DNS records, open findings and issues that could increase the blast radius of an attack.

  • Subdomain and DNS exposure
  • High-priority alerts
  • AI-assisted analysis
  • Resolve and evidence actions
02

Incident response playbooks

Clear, practical response steps for common cyber incidents, written for teams that need to act quickly.

  • Ransomware
  • Business email compromise
  • Malware and account compromise
  • Custom playbooks
03

Tabletops and incident recording

Create scenarios, run exercises, record decisions and track the actions that prove improvement over time.

  • Custom or AI-generated scenarios
  • Injects, notes and timelines
  • Post-mortem outputs
  • Actions and maturity tracking

Reduce blast radius

Small teams need fewer dashboards and clearer next steps.

The platform is designed to help you identify exposure, prepare your response, practise the uncomfortable decisions and record what happened when something goes wrong.

Attack surface monitoring

Find issues before they become incidents.

Alerts are written in plain language, with recommendations that help the team understand the issue, fix it and record closure.

  • Prioritise high-risk exposure such as dangling DNS records.
  • Use AI analysis to explain impact and recommended action.
  • Resolve findings and keep a record of what changed.
ASM alert showing a vulnerable subdomain takeover via dangling Azure CNAME

Response playbooks

Give people a place to start during an incident.

Pre-built and custom playbooks help your team respond to common incidents without starting from a blank page.
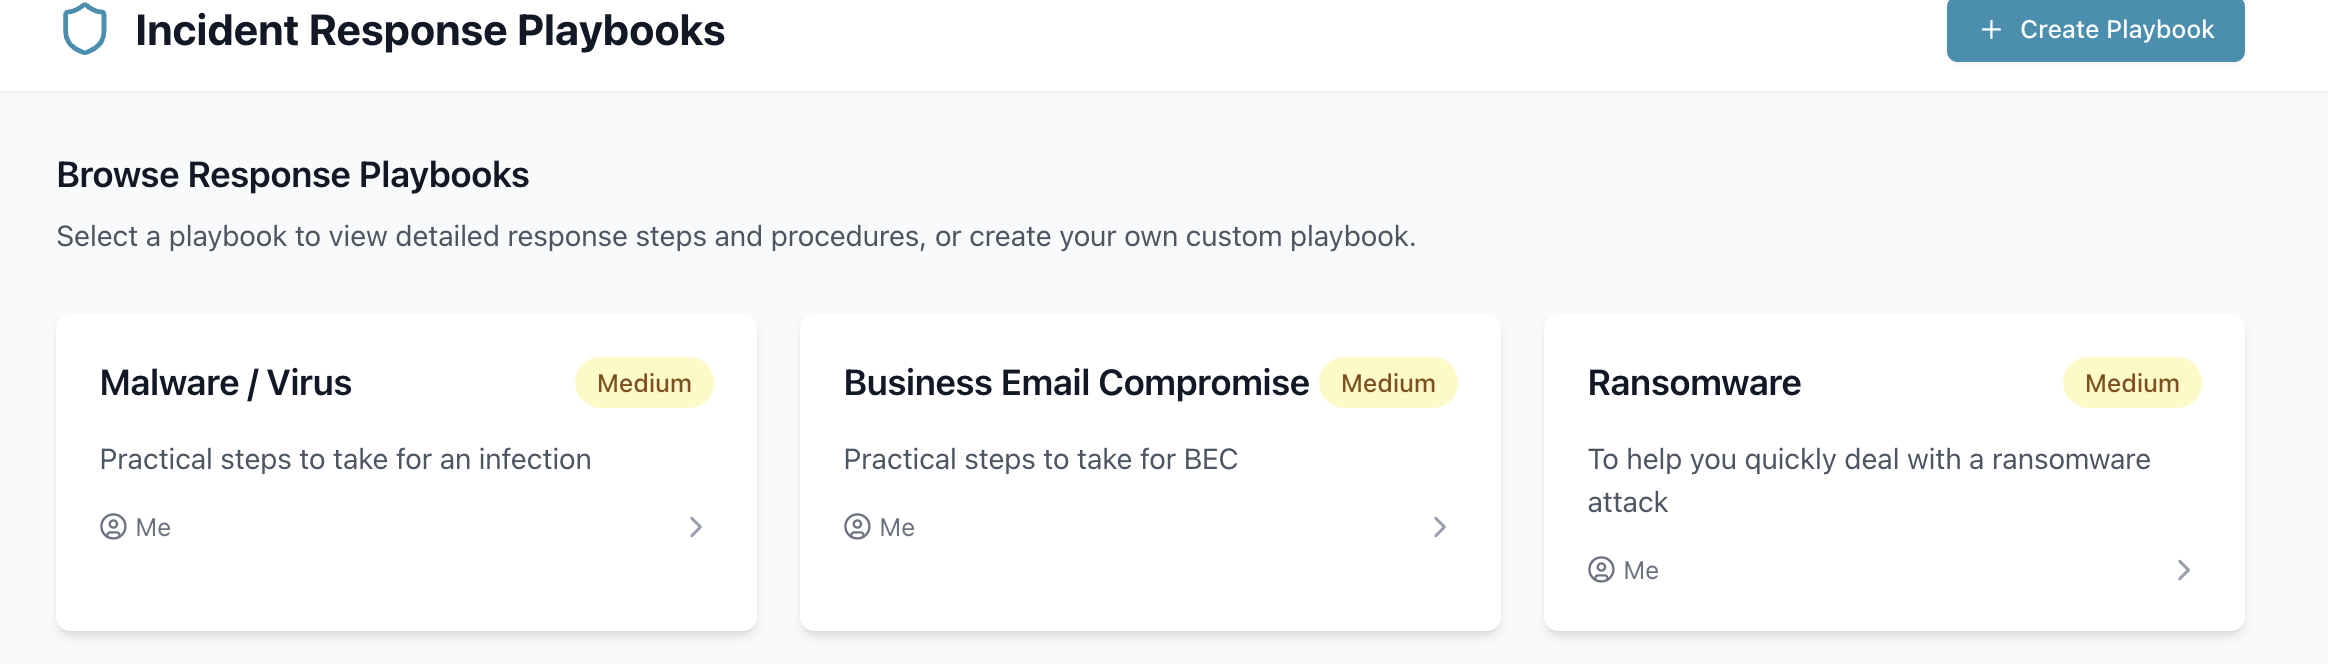
  • Ransomware, malware and business email compromise playbooks.
  • Create custom playbooks for your own environment.
  • Use playbooks during exercises and real incidents.
Incident response playbooks for malware, business email compromise and ransomware

Incident recording

Record the facts while they are still fresh.

Capture incidents, decisions, owners, status and evidence in one place, then export what you need for leadership, insurers or internal review.

  • Create and manage incident records.
  • Filter by severity, status and category.
  • Export evidence and keep post-incident actions visible.
Incident recorder dashboard with new incident, filters and export options

Why it exists

Enterprise security advice is easy to give. Smaller organisations need something they can actually run.

We care about helping organisations improve, not overwhelming them with enterprise tooling they cannot afford, staff or maintain.

Before

Identify exposed services, risky DNS records and basic weaknesses that could make an attack easier.

During

Use playbooks and incident records to capture facts, decisions, actions and ownership.

Practise

Run tabletop scenarios with injects, notes, timelines and post-mortems.

Improve

Track remediation actions and re-run scenarios to measure whether maturity has improved.

No enterprise complexity Practical cyber resilience Evidence for customers and insurers Built for smaller teams

Who it is for

For teams that need to improve security without pretending they are a bank.

Designed for realistic budgets.

Not every organisation has a large SOC, dedicated CTI function, incident response retainer and enterprise GRC platform. This gives small and mid-sized organisations a practical place to start.

  • SMBs and growing businesses
  • Fintechs, SaaS providers and professional services
  • Organisations answering customer or insurer cyber questions
  • Teams that need to prove they have practised and improved

Contact

See whether it fits your organisation.

Tell us what you currently use for exposure monitoring, playbooks, tabletop exercises and incident recording. We will show you where the platform can help and where it may not be the right fit.